EthicsComputer is an engineering-first technology house operating at the convergence of custom software architecture, proactive offensive cybersecurity (VAPT), and autonomous AI automation. We design resilient systems built around real business constraints, not fragile novelty.
Built around genuine problems, not technology fads.
Central Engineering Thesis
“A technology stack is never an end in itself. It is merely the instrument chosen to satisfy an architectural constraint. When you respect the constraint, the architecture remains timeless.”
EthicsComputer was established on February 1, 2018, in Rohtak, Haryana, initially operating as an elite technical advisory focused strictly on ethical hacking, vulnerability assessments, and defensive cybersecurity consulting. In our early audits of enterprise software, we noticed a recurring vulnerability: organizations were treating security as a cosmetic patch applied at the final hour rather than an organic property of the underlying engineering.
As clients sought our guidance not only to uncover architectural flaws but to remediate and rebuild their core systems, EthicsComputer expanded naturally into custom software development and enterprise platform engineering. Rather than assembling fragile dependencies or deploying generic off-the-shelf templates, our engineers began architecting web applications, custom databases, and proprietary operational platforms directly from first principles.
Today, EthicsComputer stands at the intersection of custom software engineering, offensive security audits, and intelligent AI automation. We do not view ourselves as an agency that trades generic development hours. We act as a dedicated technology partner taking rigorous accountability for how modern digital systems are designed, secured, deployed, and scaled over their entire lifespan.
Zero Offshore SubcontractingMutual Non-Disclosure (NDA) StandardDirect Architect Communication
EC / 03 · CAPABILITY MATRIX
One Sovereign Firm. Four Core Engineering Disciplines.
Interconnected engineering practices structured to take an architectural concept to an enterprise-grade, verified digital fortress.
DISCIPLINE 01
Custom Software & High-Concurrency SaaS
We design bespoke software solutions engineered for maintainability, high concurrency, and long service lifespans. We avoid fragile dependencies and prioritize clean modular boundaries, structured databases, and scalable backend services.
Custom Web AppsMulti-Tenant SaaSHigh-Performance APIsPostgreSQL / MySQL
Security is embedded in our DNA. We perform end-to-end vulnerability assessments and penetration testing (VAPT), manual source code audits, zero-trust network hardening, and compliance verification following OWASP Top 10, CERT-In, and ISO 27001 standards.
Web & Network VAPTSource Code ReviewZero-Trust HardeningCertified CEH Practice
We construct practical AI applications that automate mission-critical business workflows. From self-hosted Retrieval-Augmented Generation (RAG) engines that secure internal enterprise knowledge to agentic pipelines that eliminate operational friction without data leakage.
Different problems need different engineering decisions.
We reject dogma. Instead of forcing every enterprise problem into a pre-baked agency template, our engineering path begins with uncovering the real operational and security constraints.
STEP 01DISCOVERY
01. PROBLEM
Isolate the root operational bottleneck or risk surface before writing a single line of code.
STEP 02ANALYSIS
02. UNDERSTAND
Document data dependencies, compliance criteria, latency limits, and concurrency bounds.
STEP 03ARCHITECT
03. CHOOSE
Select the simplest, most stable technology primitives fitted to the problem requirement.
STEP 04ENGINEERING
04. BUILD
Construct clean, maintainable, modular software with fully automated test fixtures.
STEP 05VAPT AUDIT
05. SECURE
Subject every interface to offensive penetration testing, static code analysis & VAPT.
STEP 06PIPELINES
06. AUTOMATE
Streamline continuous delivery, deployment monitoring, and automated event notifications.
STEP 0799.98% SLA TELEMETRY
07. IMPROVE & SCALE
Monitor real production telemetry, latency logs, and server health to iteratively optimize based on live usage metrics.
EC / 05 · NON-NEGOTIABLES
Principles we refuse to compromise.
Core engineering doctrines that govern every technical decision, architecture document, and line of code we write.
01
CLARITY FIRST
Understand the problem before building the solution. Writing code without understanding the operational constraints is the fastest path to compounding technical debt.
02
MAINTAINABILITY
Build systems that can actually be maintained. We design modular architectures with clear boundaries so that systems can be debugged, refactored, and grown without friction.
03
STRUCTURAL SECURITY
Treat security as a fundamental property of code, never an afterthought. Vulnerabilities are structural defects. We harden input vectors, sessions, and APIs by default.
04
PRACTICALITY
Choose technology based on the problem, not market hype. Novelty is not a feature. We rely on proven, performant primitives that solve the exact requirement reliably.
05
ACCOUNTABILITY
Take unvarnished responsibility for what gets built. We don't hide behind ambiguous scope clauses; we own the resilience, latency, and correctness of our systems.
06
EVOLVABILITY
Build software that can adapt as your business changes. Commercial realities shift; clean interfaces and decoupled data structures ensure longevity without rewrites.
EC / CONTRAST · SYSTEM LEVEL
Why this approach matters to your balance sheet.
The difference between writing code and engineering an enterprise system is the difference between an ephemeral expense and an enduring capital asset.
CONVENTIONAL DIGITAL AGENCY
Building Software as an Agency
Pre-packaged stacks: Forcing every client requirement into the same agency boilerplate.
Post-launch security: Treating security as an afterthought or an optional checklist item.
Feature accumulation: Piling unvetted third-party plugins that degrade performance and introduce attack vectors.
Handoff & disconnect: Delivering code that requires an external team to decipher, debug, and patch.
VS
ETHICSCOMPUTER ENGINEERING HOUSE
Engineering an Enterprise Asset
Domain modeling: Designing database schemas and system interfaces around actual operational constraints.
Hardened by default: Fusing offensive threat modeling and zero-trust authentication into early architectural designs.
Maintainable primitives: Writing concise, modular, and documented code that your team can run and understand with ease.
Enduring outcomes: Taking direct responsibility for scalability, uptime, and business continuity over the long term.
EC / 06 · PEOPLE & LEADERSHIP
Behind the systems are engineers who care.
No faceless brokers or outsourced handoffs. Direct oversight by technical practitioners with hands-on production engineering experience.
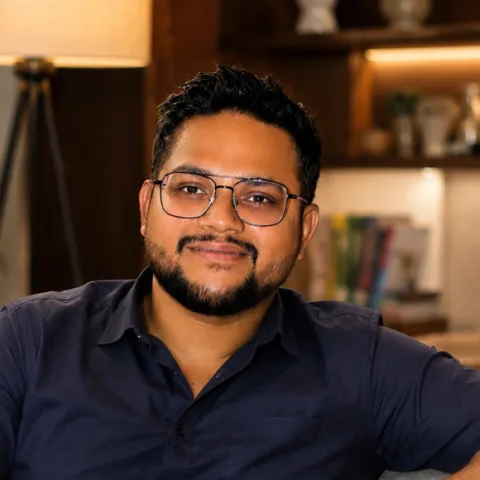
FOUNDER · ARCHITECT
Vinay Grover
Founder & CEO
Offensive Cybersecurity, Enterprise Architecture & AI Integration
Verifiable milestones tracing our evolution from an offensive cybersecurity practice in Rohtak into a nationwide enterprise technology powerhouse.
01 FEB 2018
The Genesis — Cybersecurity Advisory
Founded in Rohtak, Haryana, with a strict technical focus on Ethical Hacking, Web Application Penetration Testing (VAPT), and defensive infrastructure consulting for emerging enterprises.
LATE 2018
Software Division Launch & Proprietary Platforms
Expanded operations from vulnerability identification into active remediation and custom enterprise software development. Designed and deployed our first proprietary full-stack enterprise HRMS.
2021
AI Integration & Cloud DevOps Infrastructure
Integrated machine learning pipelines, cloud-native DevOps architectures (AWS & GCP), and automated testing suites into our core development cycles for regional and international enterprise clients.
2024 — PRESENT
AI Innovation Lab, KhataFlow & Pan-India Scale
Formalized the dedicated AI Innovation Lab for private RAG pipelines, fine-tuned domain models, and intelligent workflow automation. Launched KhataFlow CA-grade enterprise accounting and expanded nationwide enterprise deployments.
EC / 09 · VERIFIED REGISTRY
Compliance, standards & certifications.
Industry benchmarks and verified standards governing our software architecture, security practices, and infrastructure deployments.
ISO CERTIFIED ORGANISATION · VERIFIED CERTIFICATES
ISO CERTIFIED Quality Management
ACTIVE
STANDARD
ISO 9001
Quality Management Systems
Demonstrates our commitment to consistent quality delivery, customer satisfaction, and continual process improvement across all software engineering and service operations.
Certifies our structured approach to IT service delivery with defined SLAs, incident management, change control, and continuous improvement across enterprise client deployments.
Our highest-assurance security certification — validates rigorous controls over data confidentiality, integrity, and availability for all client systems, code repositories, and cloud infrastructure.
Web application security aligned with OWASP Top 10 across all code audits, VAPT engagements, and secure SDLC practices.
STANDARD 02
GDPR & DPDP 2023
Privacy-by-design architectures ensuring compliance with global and Indian statutory data protection mandates.
STANDARD 03
CEH Audited Practice
Certified Ethical Hacker offensive methodology utilized for comprehensive vulnerability testing and code audits.
STANDARD 04
Cloud Ecosystem
Architectures aligned with AWS Well-Architected and Microsoft Partner enterprise infrastructure guidelines.
EC / QUESTIONS & ARCHITECTURAL TRUTHS
Frequently Answered Questions
Direct, honest answers about our background, engagement criteria, and engineering philosophy.
EthicsComputer was founded on February 1, 2018, with registered engineering headquarters in Rohtak, Haryana, India (124001). Today, we operate across all 36 States and Union Territories of India, engineering resilient systems for high-growth enterprises, regulated institutions, and innovative technology ventures.
We are an engineering and offensive cybersecurity house, not a WordPress template shop or marketing reseller. We build architectures from first principles with zero-trust security harnesses, dedicated CERT-In/OWASP VAPT audits, modular databases, and sovereign in-house code. We take direct accountability for uptime, latency, and system integrity.
Yes. Our offensive security engineers and Certified Ethical Hackers (CEH) carry out rigorous Vulnerability Assessment and Penetration Testing (VAPT) strictly aligned with CERT-In recommendations, OWASP Top 10, NIST SP 800-115, and ISO/IEC 27001 standards. Every engagement delivers verifiable remediation verification.
EthicsComputer has engineered proprietary enterprise platforms including EthicsHRMS (enterprise biometric attendance, automated compliance & payroll engines), KhataFlow (CA-grade double-entry accounting & automated bank reconciliation), and real-time security threat telemetry scanners.
We reject superficial novelty. We construct domain-specific private RAG (Retrieval-Augmented Generation) pipelines, deterministic workflow agents, and self-hosted LLM inferences that integrate directly with enterprise databases, ERPs, CRM platforms, and WhatsApp Business APIs with zero data leaks.
Engagements start with a structured technical discovery and mutual NDA. You can contact our engineering desk directly at +91 90532 10052, email us at info@ethicscomputer.in, or submit an intake consultation on our secure portal.
EC / 11 · DIRECT ENGAGEMENT DESK
Have a system worth engineering right?
Tell us about your technical landscape. We'll start with the operational constraints, execute a signed NDA, and build an architecture that survives the next decade.
Receive a preliminary project architecture, pricing tiers, and timeline estimate within 24 hours under strict NDA.
Consultation Scope Confirmed!
Your architecture brief has been dispatched directly to our Senior Technology Lead. Expect an initial feasibility analysis and callback within 24 hours under strict NDA.